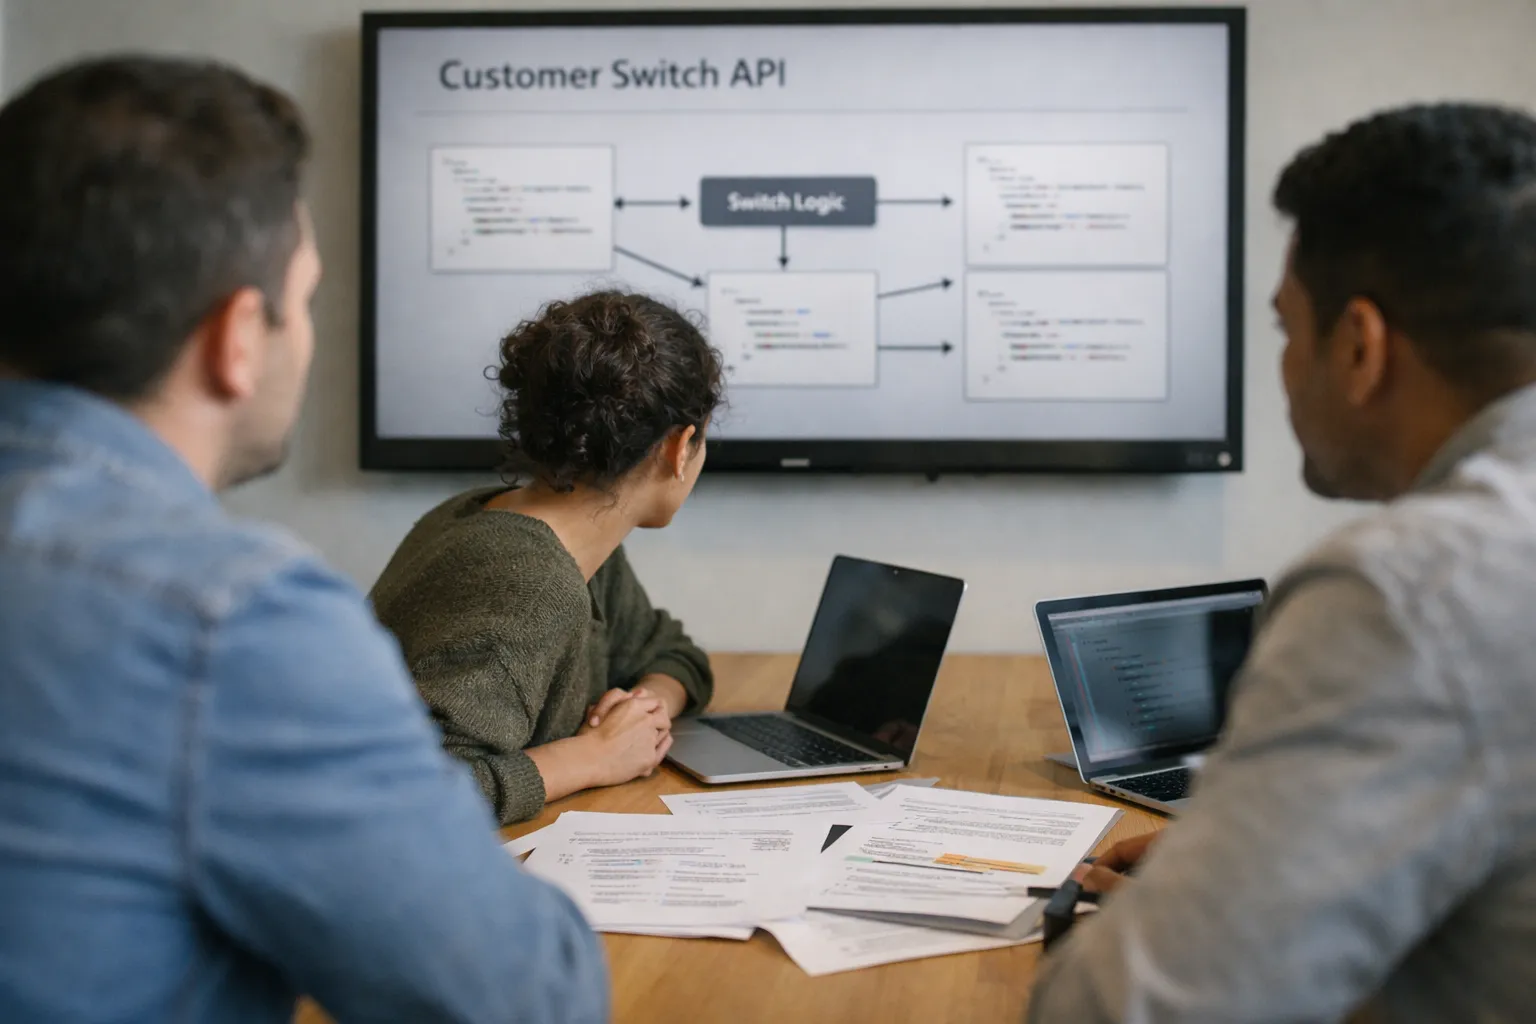
Brussels has taken a consequential step for the SaaS market: final guidance tied to the Digital Markets Act (DMA) published in late June 2026 clarifies how the law applies to business-to-business software platforms. The guidance makes explicit that designated gatekeepers offering SaaS must provide standardized, machine-readable data exports and a set of customer‑switch APIs that enable customers to transfer operational data and switch providers with minimal friction.
What the guidance requires — in plain terms
The guidance translates DMA obligations—originally aimed at large consumer platforms—into concrete expectations for enterprise SaaS vendors that meet gatekeeper thresholds. Key elements include:
- Standardized data exports: Customers must be able to obtain their operational, billing, and configuration data in open, machine-readable formats without manual intervention. Exports should include metadata and mapping that explain data schemas.
- Customer‑switch APIs: Vendors must offer authenticated APIs that allow a customer or an authorized replacement service to ingest exported data and re-establish configuration, integrations, and access controls.
- Interoperability hooks: Where reasonable, SaaS gatekeepers should expose APIs for commonly used integrations (e.g., identity providers, billing systems, analytics hooks) so integrations can be reattached on a new platform without a full rewrite.
- Timeliness and cost limits: Exports and switch processes must be delivered within specified timeframes and cannot be subject to excessive fees that would effectively lock customers in.
- Transparency & documentation: Full technical docs, SDKs and a published SLA for transfer operations are required to ensure the process is predictable for customers and migration partners.
Why this matters for SaaS vendors and buyers
For large SaaS vendors who are designated gatekeepers under the DMA, the guidance removes ambiguity. Previously, vendors could point to portability clauses in contracts while keeping exports effectively unusable due to opaque formats, partial dumps, or missing metadata. Regulators now expect practical portability — not just a ZIP file of CSVs.
For customers, especially enterprise buyers with complex integrations and compliance needs, the change lowers the operational cost and risk of switching suppliers. Where switching previously involved months of engineering effort, the guidance aims to reduce that to weeks in standardized scenarios.
Immediate operational impacts
- Platform engineering teams must inventory the data, configuration and integration artifacts that customers need to keep operational capability when migrating.
- Product teams will need to design and publish versioned, authenticated APIs for exports and imports and to provide SDKs or partner connectors for common migration pathways.
- Security teams must review authentication models for delegation (so replacement services can act on behalf of customers) without weakening access controls.
- Billing and legal teams must update contracts, pricing and SLAs to reflect new obligations.
How vendors can comply without breaking their product
Compliance will be easier for vendors that plan proactively. Practical steps include:
- Map customer-critical assets: Create a prioritized inventory of tenant data, configuration, integrations, and artifacts (templates, workflows, access policies).
- Define canonical formats: Adopt or publish canonical schemas for each asset class. JSON Schema, OpenAPI payloads and industry formats (e.g., SCIM for identity data) reduce friction.
- Build authenticated, idempotent transfer APIs: APIs should support resumable exports, chunked transfers and clear status reporting so large migrations succeed reliably.
- Provide partner SDKs and migration docs: Practical SDKs for target platforms and clear runbooks shorten migration time and reduce support load.
- Offer a migration sandbox: A temporary environment where customers can test imports accelerates verification and reduces operational risk.
Commercial and strategic consequences
Complying with the DMA guidance is not purely an engineering exercise. Vendors will face short-term costs for platform work and documentation. But there are commercial opportunities: vendors that make portability painless can use it as a competitive advantage in procurement processes, and a predictable switch process may reduce the need for heavy discounts to retain customers.
For ISVs that fear churn, two practical defenses work better than proprietary lock-in: increasing switching costs through differentiated features (not by obstructing exports) and building deeper integration of business processes into customers’ workflows—features that are harder to replicate than an export file.
What buyers and migration partners should do now
Enterprise buyers should treat portability as a procurement metric. RFPs should require:
- Machine‑readable export examples
- API documentation and SLA commitments for transfer operations
- Proof of prior migrations or reference customers
Migration services and systems integrators should accelerate toolchain development: reusable connectors, verification tooling, and automated reconciliation will be in demand as customers evaluate replacement scenarios under shorter timelines.
Remaining questions
The guidance leaves some open questions for which vendors and buyers will seek clarity from regulators and industry bodies: cross-border data transfer constraints, edge cases for joint-data ownership across ecosystems, and how regulators interpret “reasonable cost.” Expect further clarifications and possibly technical standards from EU bodies or industry consortia over the coming months.
For SaaS vendors operating at scale in Europe, the message is clear: portability is no longer an optional nicety. It’s a regulatory expectation—and the companies that implement it well will turn compliance into a commercial differentiator.