Who, what, when, where, why: As of August 2026, enforcement activity tied to the European Union’s AI Act is firmly reshaping product roadmaps and procurement in the SaaS market. Across the EU and in contracts with European customers, vendors embedding generative‑AI “copilot” features now face routine demands for model documentation, human‑in‑the‑loop controls, regional hosting, and demonstrable auditability — or longer sales cycles and potential regulatory scrutiny under penalties that can reach €35 million or 7% of global turnover.
Why this matters now
The Act’s risk‑based framework hasn’t changed since earlier this year, but the market has. From June to July 2026 we watched the theoretical become operational: enterprise buyers added AI disclosure line items to RFPs, procurement teams started to insist on packaged compliance artifacts, and engineering teams moved compliance work from backlog to sprint. If you sell a copilot into Europe, treating the AI Act as future work is a losing strategy — it now determines whether you get to compete.
New data and vendor trends (July 2026 survey)
SaaS Review Hub surveyed 220 European‑facing SaaS vendors in July 2026. Key findings:
- EU modes are now standard: 78% report offering explicit opt‑in toggles or per‑tenant controls for generative features, up from 62% in April.
- Regional hosting expected: 61% provide EU‑only hosting for inference or model weights (versus 48% in April).
- Documentation is table stakes: 84% publish model cards, risk summaries, or transparency statements accessible to procurement teams.
- Audit logging is mainstream: 57% retain structured inference logs and metadata to support conformity assessments.
- Third‑party stacks grow: 48% now rely on third‑party compliance tooling (explainability modules, model registries, impact‑assessment pipelines).
- Feature restriction persists: 33% of vendors have delayed or limited generative features in the EU pending additional compliance investment.
What’s changed in practice
Three developments matter more than incremental policy shifts:
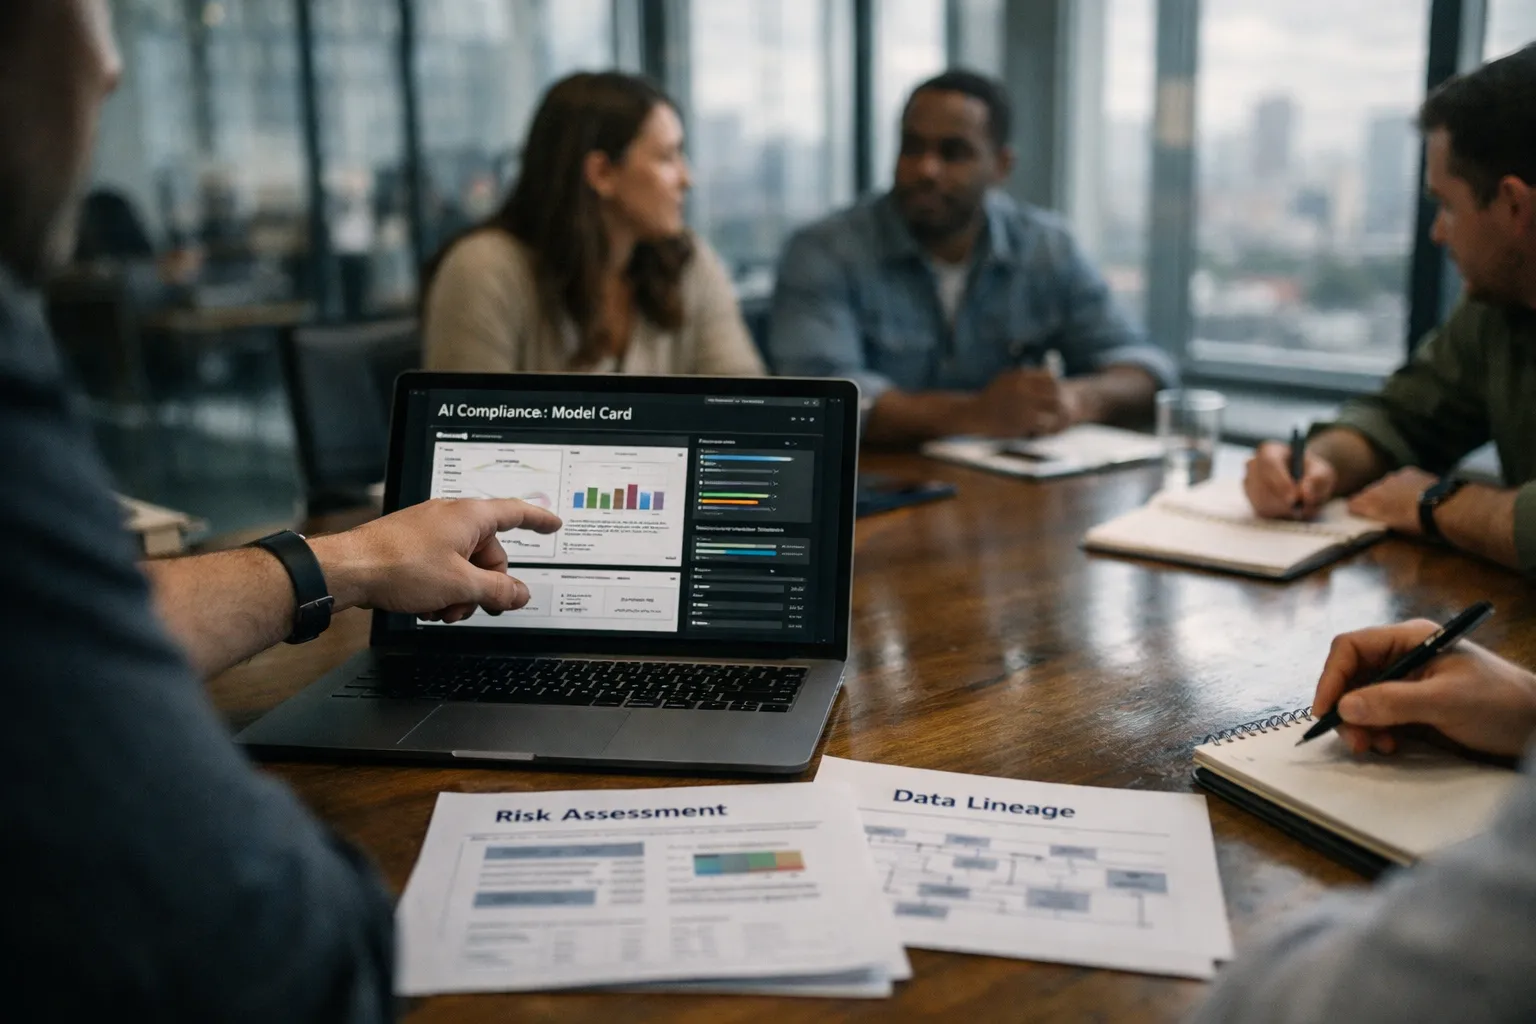
- Procurement templates now include AI clauses: Large enterprises and public buyers routinely request a “compliance package” (model card + risk assessment + logging policy + human‑review SOP).
- Assurance markets emerged: There’s a growing market for AI conformity attestations from both traditional auditors (Big Four firms offering AI assurance) and specialist providers offering SOC‑style reports focused on model controls.
- Cloud providers are a strategic lever: Vendors that leverage AWS, Google Cloud, or Microsoft Azure regional model services get faster to market because these platforms now provide standardized audit artifacts and data‑residency options.
Operational and commercial impact
Engineering roadmaps now include observability, lineage, and tamper‑resistant logging as first‑class features. Product teams are forced to choose: ship full capability and pay the compliance tax, productize a “compliance edition” targeted at EU customers, or limit EU availability. Commercially, sales cycles that once closed in weeks are routinely taking months when AI features are central — unless the vendor arrives with a ready compliance package.
"Companies that treat compliance as product are winning deals; the rest are explaining why they can't," says Laura Chen, Senior Analyst at SaaS Review Hub.
Concrete examples and vendor patterns
- Large incumbents: Many reuse cloud providers’ regional model services and prebuilt audit artifacts to present a neat compliance story to procurement.
- Mid‑market compliance editions: Vendors are launching EU‑focused tiers that include logging, guaranteed human‑review SLAs, and contractual model‑use restrictions.
- Startups choose fast follow or narrow scope: Some startups restrict generative features for EU customers or delay launches until they can afford third‑party attestations.
Updated cost picture
Compliance costs have crept higher. In our July 2026 survey smaller vendors reported median first‑year compliance costs in the €120k–€400k range (engineering, legal, documentation, and external assessments), depending on model complexity and customer base. Reusing cloud tooling and buying packaged compliance services still cut costs materially versus building from scratch.
Updated action checklist — August 2026
- Inventory and classify now: Map AI touchpoints by customer, region, and decision impact. Flag features that could trigger high‑risk classification (automated hiring, credit scoring, legal advice).
- Ship a procurement package: Publish succinct model cards, a risk assessment summary, and a logging policy in a single downloadable bundle for buyers.
- Offer configurable residency and opt‑ins: Provide per‑tenant controls (EU inference vs. global), default conservative settings, and clear opt‑in flows for copilots.
- Build observable, privacy‑aware audit trails: Capture model version, input/output hashes, timestamps, and decision metadata while applying data‑minimization and encryption at rest.
- Operationalize human oversight: Define mandatory review thresholds, surface confidence indicators, and log overrides for auditability.
- Plan for external assurance: Budget for external attestations or SOC‑style AI reports; many buyers now ask for them during late‑stage procurement.
- Update contracts: Add AI clauses to DPAs, include incident‑notification SLAs, and package compliance artifacts into a repeatable sales playbook.
Who benefits — who pays
Vendors with compliance budgets and cloud relationships benefit: they can absorb tooling costs and publish repeatable artifacts. Mid‑market firms that productize compliance can win risk‑averse accounts. Early‑stage startups face the hardest choices — limited EU TAM or higher contractual liability — unless they reuse cloud controls or buy third‑party assurance.
Reactions from the field
Procurement teams tell us they’re tired of vague answers. Engineers say the work is practical but time‑consuming. Legal teams are scrambling to translate model behavior into contract terms. The bottom line: transparency and configuration shorten sales cycles; opacity lengthens them.
What's next — what to watch
- Wider adoption of third‑party AI assurance reports (SOC‑style and attestations) in RFPs.
- More specific guidance from national supervisory authorities clarifying borderline cases for "influence" vs. "decision."
- Broader use of on‑device or edge inference to limit data export where feasible.
Do I have to treat every copilot feature as high‑risk?
No. The AI Act is risk‑based: only some uses trigger the strictest obligations. But many transparency and documentation duties apply broadly. Inventory and classification are non‑negotiable first steps.
Can regional hosting alone avoid obligations?
No. Data residency helps but doesn't automatically remove obligations. If your service is offered to — or affects — EU users, transparency, documentation, and oversight duties will still apply in many cases.
What proof do buyers expect today?
Buyers increasingly ask for a compliance package: model cards, risk‑assessment summaries, logging and lineage statements, human‑in‑the‑loop policies, and — increasingly — a third‑party attestation or SOC‑style AI report.
How much should startups budget for compliance?
Survey median first‑year ranges are now €120k–€400k for smaller vendors. Costs vary with model complexity and customer demands; reuse cloud tooling and consider third‑party compliance stacks to reduce spend.
The enforcement phase of the EU AI Act is here and it favors vendors who treat compliance as product strategy, not a tax. If you want to sell copilots into Europe, build that procurement package today — anything less will slow your sales and shrink your runway. We're watching this like a playoff series: teams who prepare win; the rest get cut.